Abstract network representing secure Microsoft Cloud services

Microsoft 365 Security · Compliance · Copilot Readiness

Run Microsoft 365 securely—before misconfigurations, data sharing and Copilot become a risk.

We assess Entra ID, Conditional Access, Intune, Defender, Purview and Microsoft 365 governance, prioritize the most important risks and turn them into a practical security and compliance roadmap.

Microsoft-certified · Cologne/NRW · DACH remote · Security & Compliance specialist

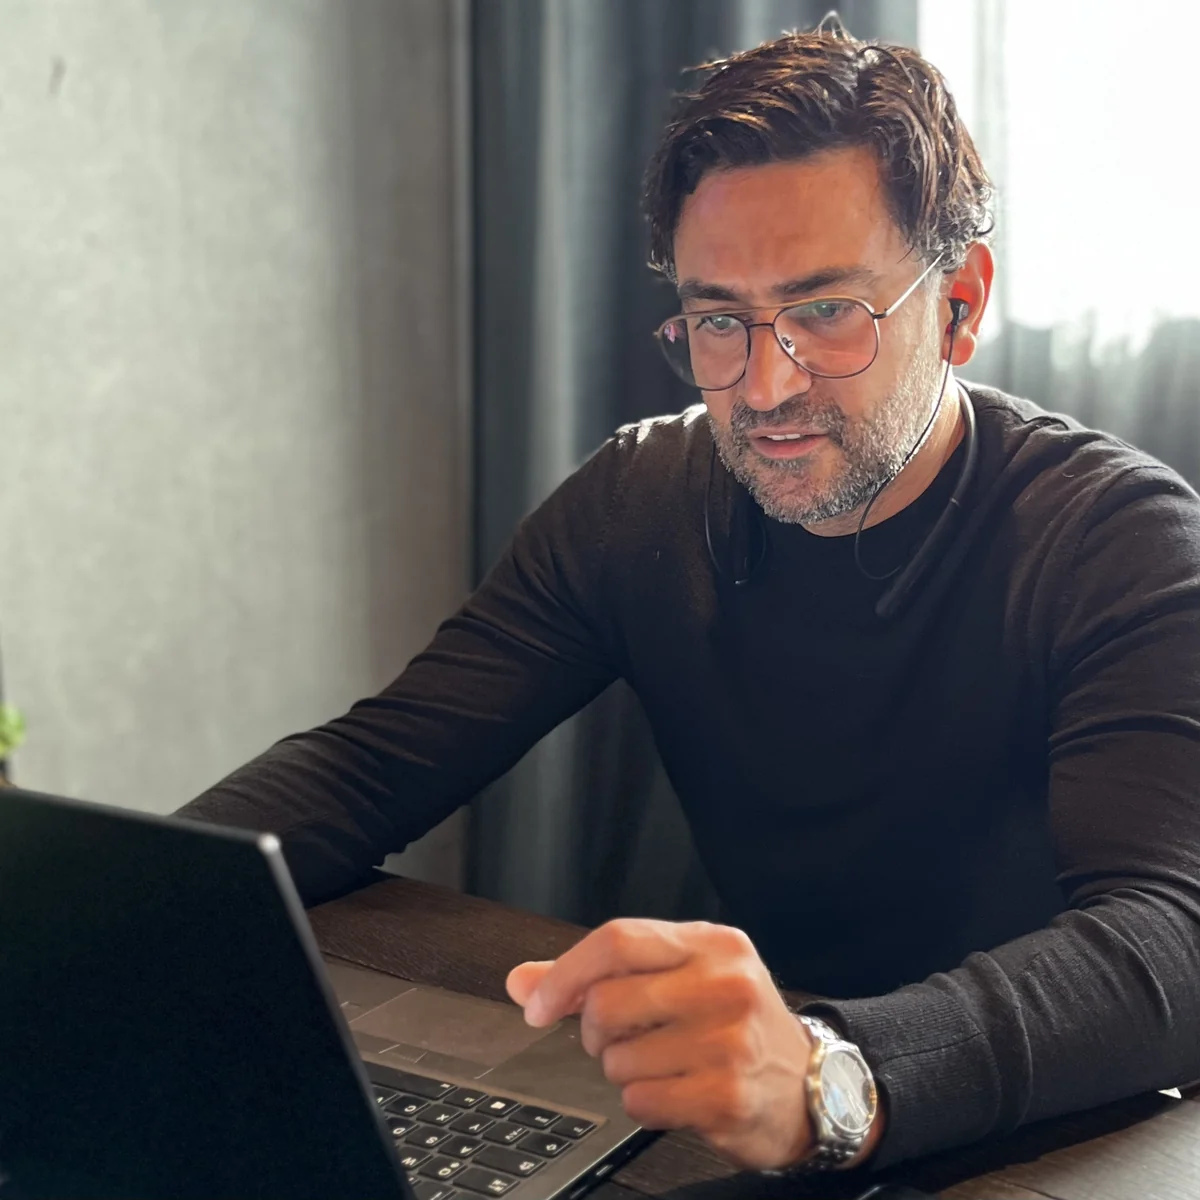
Farhad Niat working on a Microsoft cloud project

Farhad Niat

Dipl. Wirtschaftsinformatiker

Long-standing Microsoft Cloud experience from complex enterprise environments—from Microsoft 365 Security and Identity to Intune, governance, Teams and Unified Communications.

  • Microsoft specialist
  • Security-first
  • Cologne and remote across DACH

Microsoft credentials

Microsoft certifications

Four certifications covering Microsoft 365 administration, Copilot, agents, AI and Teams Voice.

View credentials on LinkedIn

Common starting points

Does this sound familiar?

The issue is rarely a single Microsoft product. It is usually accumulated configuration, unclear access and missing priorities.

01

Microsoft 365 has grown over years

No one can confidently confirm whether Conditional Access, admin roles, devices and external access are still secured consistently.

02

External sharing is difficult to oversee

Teams, SharePoint and OneDrive contain accumulated permissions, guest accounts and sharing links.

03

Copilot is about to be introduced

But it is unclear which internal information may suddenly become easier to discover.

04

Security products are in place—but not aligned

Entra ID, Intune, Defender and Purview are licensed, but policies and responsibilities have evolved historically.

Prioritize Microsoft 365 risks

Three clear entry points

Which assessment fits your situation?

Choose based on your immediate pressure to act. Every assessment provides a defensible current-state view, prioritized risks and a practical next step.

02 · Data & governance

Microsoft 365 Governance & Compliance Assessment

For established Teams, SharePoint and OneDrive structures with unclear rules.

Typical questionWho can access sensitive data—and are sharing, protection and retention governed consistently?
Assessment focus
  • Teams, SharePoint & OneDrive permissions
  • Guests, sharing links & lifecycle
  • Purview, sensitivity labels & DLP
  • Retention & responsibilities
You receiveA governance and compliance gap analysis with a prioritized action plan.
Request Governance & Compliance Assessment
03 · Copilot rollout

Microsoft 365 Copilot Readiness Assessment

For organizations preparing a Copilot pilot or broader rollout.

Typical questionWhich internal information could Copilot make discoverable to too many people?
Assessment focus
  • Permissions across SharePoint, Teams & OneDrive
  • External sharing & guests
  • Sensitive data & Purview controls
  • Pilot group, governance & rollout prerequisites
You receiveA readiness score, prioritized risks and a controlled pilot roadmap.
Request Copilot Readiness Assessment

Specialist topics such as Conditional Access, Microsoft Intune, Microsoft Purview and Microsoft Defender are derived from the assessment as implementation modules when needed.

How we work

What working with Azuric looks like.

Direct senior-level collaboration and a clear path from technical analysis to defensible decisions and practical next steps.

01Personal and accountable

One direct point of contact

Analysis, prioritization and decisions are handled directly with Farhad Niat—without handoffs to changing project teams.

02Put technology into context

Clear priorities

Findings are evaluated by risk, business impact and implementation effort.

03Turn findings into action

From analysis to implementation

You receive a realistic roadmap with concrete next steps—not a loose list of recommendations.

Anonymized insights from real projects

Enterprise experience for complex Microsoft 365 change.

Three selected project types Azuric has delivered—technically condensed and without confidential customer data or unsubstantiated metrics.

View all project examples

Next sensible step

Which Microsoft 365 risks should you address first?

We identify critical security gaps, prioritize the most important measures and turn them into a realistic security roadmap.

  • Microsoft certified
  • Direct senior-level consulting
  • Cologne/NRW & DACH remote
Request Microsoft 365 Security AssessmentNon-binding enquiry · Direct response